AM InfoWeb Completes ISMS Training: 2,000-Plus Employees, One Month
TL;DR: Key Highlights
AM InfoWeb completed ISMS training and assessments for more than 2,000 employees within one month.
Employees reviewed shared learning materials before completing individual assessments.
Employee-level records made participation and assessment completion traceable across the workforce.
Department heads owned team completion, while the training head consolidated results across departments.
Healthcare organizations entrust their information management partners with sensitive records. That responsibility extends to every employee who accesses, processes, or shares those records. Clear security policies, workforce awareness, and documented accountability are essential to managing that trust.
AM InfoWeb completed an organization-wide Information Security Management System (ISMS) training and assessment program for more than 2,000 employees within one month. The exercise combined structured learning, individual assessment tracking, and departmental ownership, with the organization’s training head consolidating completion data.
How AM InfoWeb Coordinated the Training Rollout
An ISMS establishes a framework for identifying information security risks and implementing safeguards to protect the confidentiality, integrity, and availability of information. Employee awareness supports that framework by communicating the responsibilities behind those safeguards.
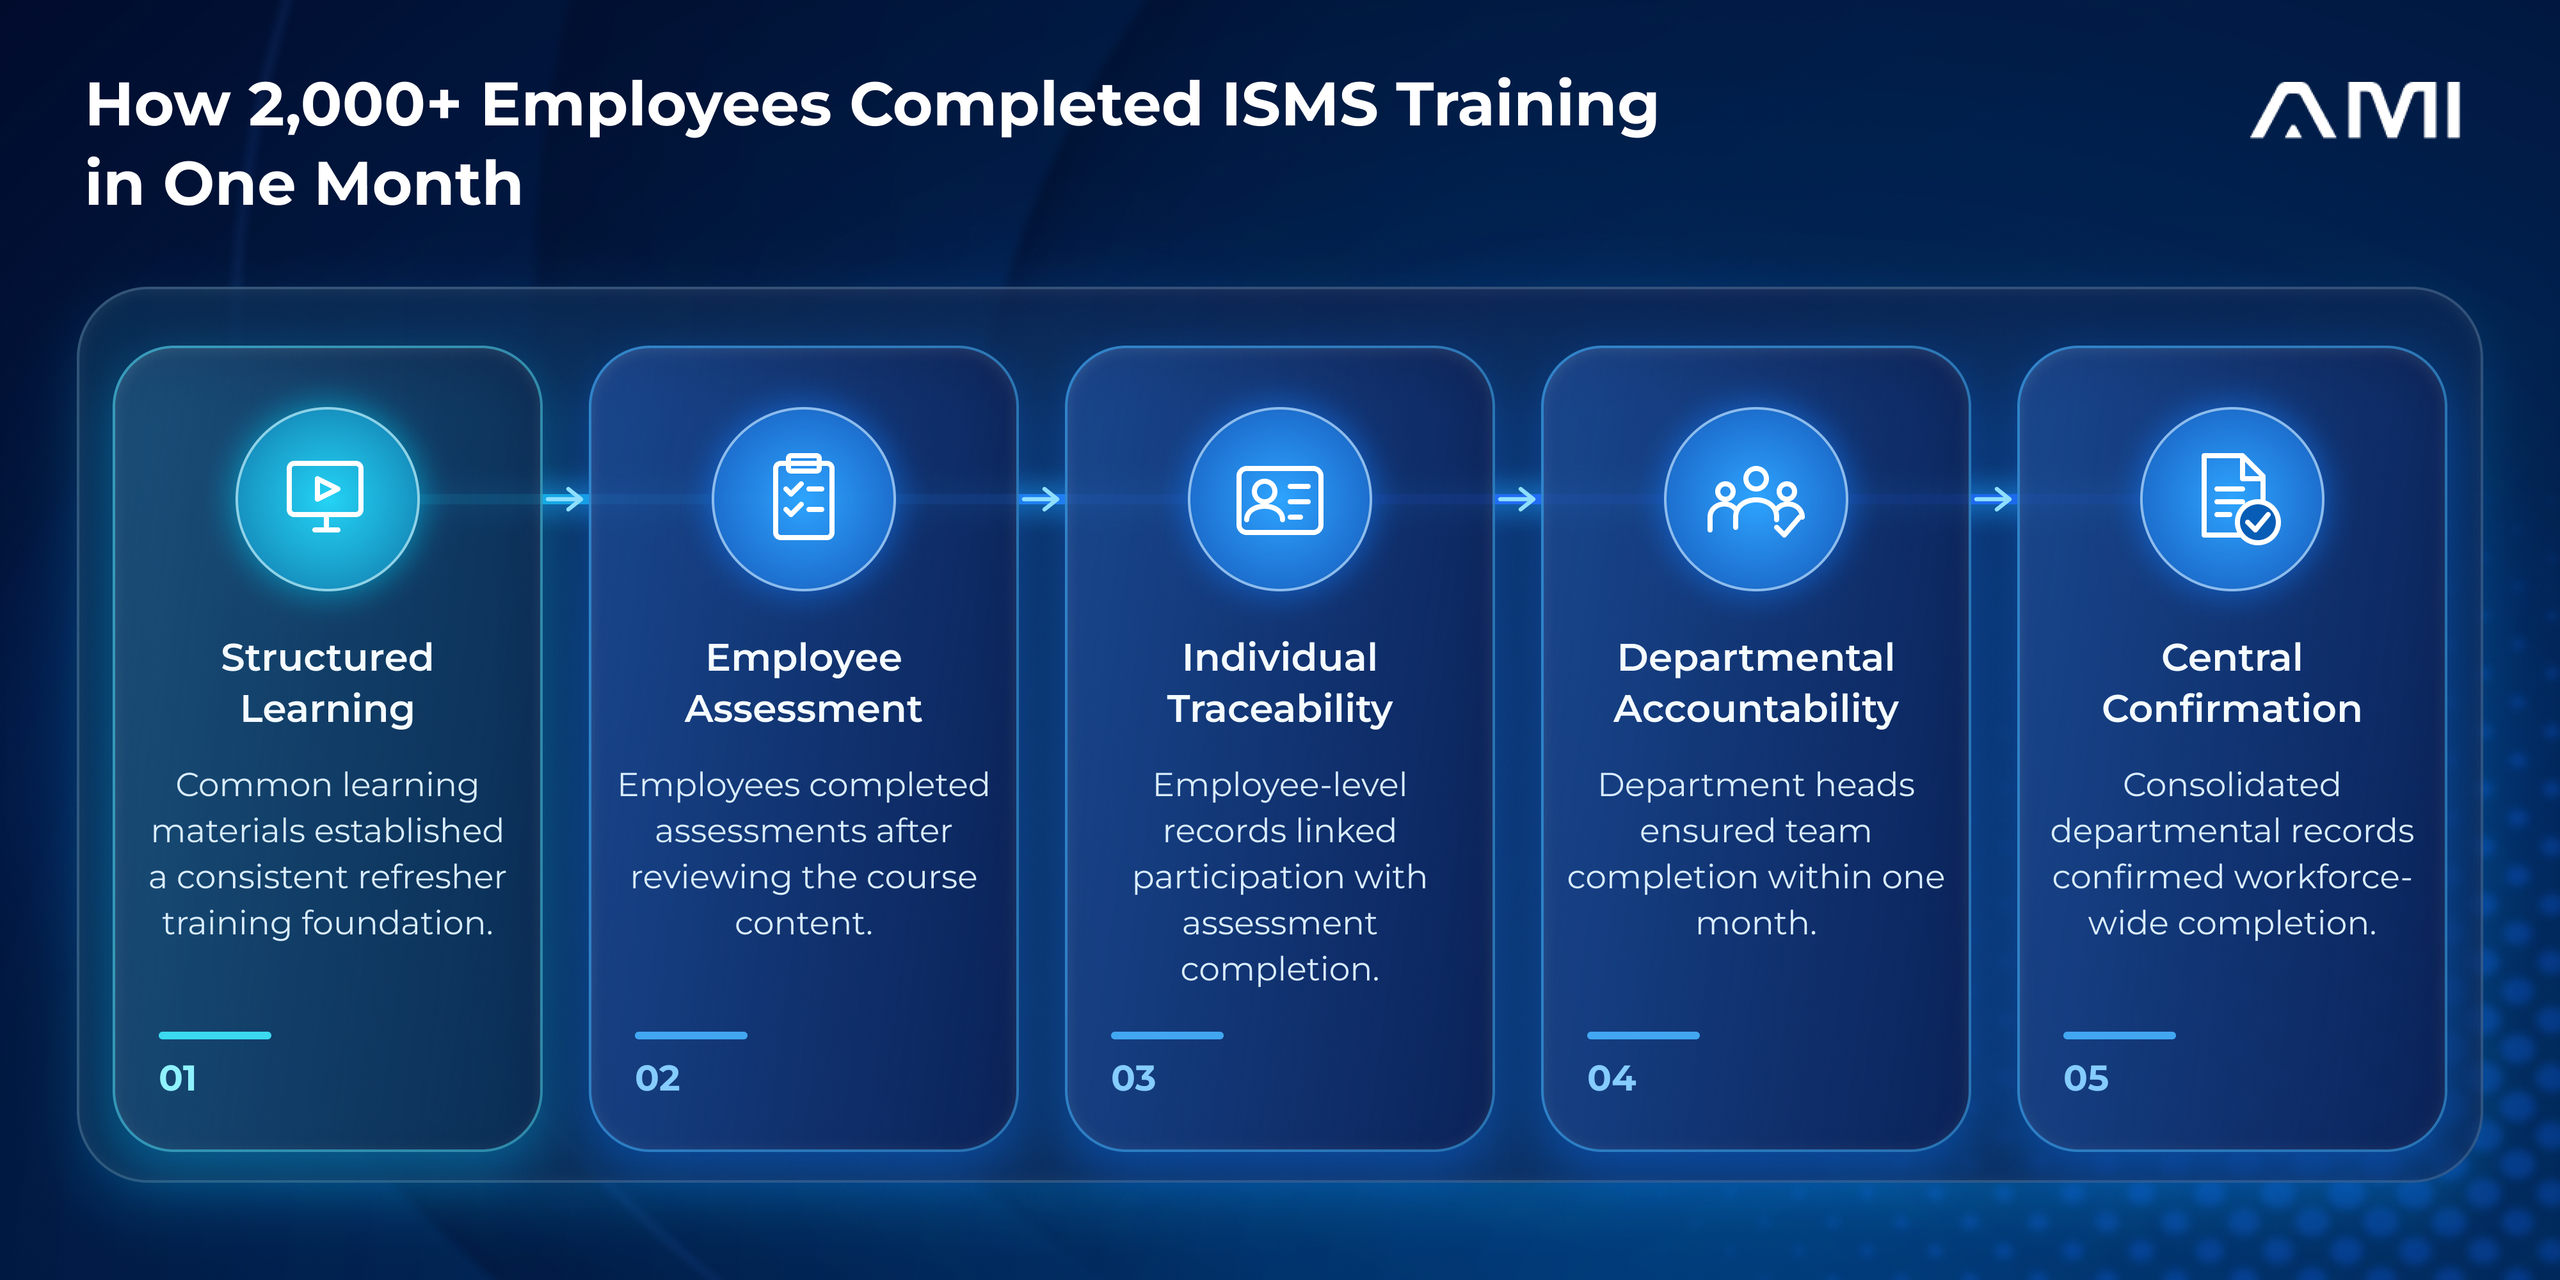
AM InfoWeb organized the training and assessment program around five steps, with departmental ownership and centralized completion tracking.
Step 1: Structured Learning
AM InfoWeb brought together ISMS learning materials, including videos, presentations, and PDF resources, into a common set of resources. These materials established what employees needed to review as a refresher before completing the assessment.
Step 2: Employee Assessment
After reviewing the learning materials, employees answered assessment questions covering the course content. This connected the learning exercise with an individual assessment whose completion could be recorded and tracked.
Step 3: Individual Traceability
Participation and assessment completion were linked to individual employees through self-supplied names and employee IDs. Employee-level records allowed AM InfoWeb to track who had completed the exercise and maintain a traceable record of participation across its workforce.
Step 4: Departmental Accountability
Each department head was responsible for ensuring that their team completed the exercise within the one-month deadline. This established clear ownership across departments and a consistent timeframe for completing the training and assessment.
Step 5: Central Confirmation
The training head collected completion data from each department and consolidated the results. This provided an organization-wide view of participation and enabled AM InfoWeb to confirm completion across its workforce.
Accountability and Completion Tracking Across a Large Workforce
Completing ISMS training and assessments for more than 2,000 employees within one month marked a significant milestone for AM InfoWeb. At this scale, the challenge was coordinating participation across departments and maintaining a clear record of completion throughout the organization.
AM InfoWeb achieved this through defined responsibilities, employee-level tracking, and centralized oversight, bringing the workforce-wide exercise to completion within the agreed timeframe.
For a large organization, these mechanics matter. Here’s how:
- A deadline establishes the expected outcome
- Departmental ownership assigns responsibility
- Employee-level records make participation traceable
- Central consolidation provides organization-wide visibility.
Why ISMS Training Matters When Handling Health Information
Health information security depends on both technical safeguards and employee decisions.
Access controls can restrict entry to a system, but employees still need to understand authorized use, secure data handling, and incident reporting.
In healthcare workflows, those responsibilities can include:
- Verifying a recipient before transferring a record
- Protecting login credentials
- Recognizing phishing attempts
- Promptly escalating a suspected disclosure
These are practical examples of the security decisions that workforce awareness programs should address.
The consequences extend beyond confidentiality. An unintended alteration can compromise data integrity, while an inaccessible record can interrupt service delivery. Security awareness therefore supports the broader responsibility to handle information accurately, securely, and reliably.
ISMS training provides a foundation for communicating these expectations. Its value is strengthened when participation is assigned, tracked, and confirmed across the organization.
Looking for a healthcare partner with clear security accountability?
AM InfoWeb completed ISMS training and assessments for more than 2,000 employees within one month. Discuss the security responsibilities and operating evidence your healthcare workflows require.
Evidence of Execution for Healthcare Buyers
For organizations evaluating a health information management partner, broad statements about security offer limited insight into implementation. Specific operational evidence is more useful.
AM InfoWeb’s program demonstrates how it coordinated a workforce-wide security learning exercise: a common set of materials, an assessment, a defined completion window, accountable department heads, and individually traceable participation.
These practices are relevant to the people and governance dimensions of an ISMS. ISO/IEC 27001 establishes requirements for managing information security through an organization-wide approach encompassing people, processes, and technology. Workforce training supports that approach, alongside technical controls and ongoing risk management.
Training completion is one measure within a wider security program. AM InfoWeb’s achievement provides concrete evidence of its ability to organize and account for employee participation at scale. This is a meaningful consideration for clients assessing how a partner communicates information security responsibilities throughout its business.
Frequently Asked Questions
About the Author
Written by
Urza Dey
Urza Dey is a content and copywriter with over five years of experience across marketing, B2B SaaS, HealthTech, EdTech, and related industries. At AMI, they contribute to content strategy, blog development, and marketing communication focused on healthcare operations, business process management, and AI-enabled service delivery.